
University of New Mexico Health Sciences Center Grapples with Significant Cyber Incident
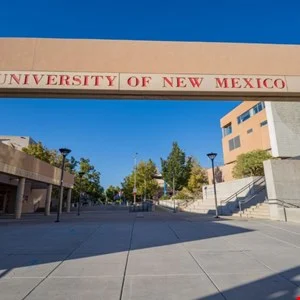
The University of New Mexico Health Sciences Center (UNM HSC) recently faced a severe operational disruption following a major cyber incident that forced the institution to halt medical services, divert emergency traffic, and suspend academic operations. The breach, which prompted an immediate and high-level response from the medical center’s administration, serves as a stark reminder of the escalating threat landscape facing the healthcare and academic sectors, where the intersection of sensitive patient data and critical infrastructure creates a prime target for malicious actors.
The incident was first disclosed to the public on the afternoon of Monday, October 26. At approximately 2:30 p.m. MDT, the leadership at UNM HSC issued an urgent advisory to patients and staff, signaling that the organization had fallen victim to a cybersecurity event of such magnitude that it necessitated the immediate cancellation of all scheduled appointments and surgeries for the remainder of the day. The directive was clear and prioritized safety above all else: UNM Health patients were instructed to refrain from arriving at any UNM Health facilities, and those in need of emergency care were advised to utilize 911 services, which would coordinate the necessary diversion of ambulances to other providers. Non-emergency matters, meanwhile, were placed on an indefinite hold as the center’s technical teams scrambled to assess the scope of the compromise.
"UNM Health patients should not show up to UNM Health facilities on October 26," the institution stated in an official update. "Emergencies should be handled by 911 and non-emergencies should be delayed until further notice." This blunt, necessary communication underscored the severity of the situation; in a medical environment, the loss of digital connectivity—ranging from electronic health records (EHR) to patient monitoring systems—can transform a functioning hospital into a paralyzed facility within minutes.
Clinical Services Resume Amid Ongoing Academic Disruptions
The response to the incident was swift, characterized by a phased restoration of critical services. By late evening on October 26, the administration provided a more optimistic update, announcing that the hospitals had reopened and that clinics would begin the process of returning to regularly scheduled appointments and procedures starting Tuesday, October 27. The restoration of these services was conducted with extreme caution, as the security teams prioritized the integrity of the network and the safety of patient care systems.
"At 2:30 p.m., UNM Health began resuming operations and bringing systems back online in phases, as it was safe to do so," the HSC confirmed in a follow-up statement. "We will work with patients to reschedule missed appointments and procedures." While the return to clinical operations provided a measure of relief for the local community, the impact on the university’s academic mission remained significant.
The cyberattack had far-reaching consequences for the student body and faculty. On the day of the disclosure, students enrolled in the School of Medicine, the College of Pharmacy, the College of Nursing, and the College of Population Health were instructed to clear the campus immediately. This was not merely a precautionary measure but a strategic move to isolate the network and prevent further unauthorized access while remediation efforts were underway. Non-essential employees were similarly sent home as the university moved to minimize the digital footprint across its affected campuses.
The disruption to education was not limited to the immediate aftermath of the breach. The university announced that all classes—including those held online and remotely—within the School of Medicine, College of Nursing, College of Pharmacy, and College of Population Health would remain canceled on Tuesday, October 27. This decision reflected the depth of the technical challenge, as the university sought to ensure that no compromised systems could be leveraged to interfere with academic continuity. Interestingly, the incident was localized in its impact on university life; classes at UNM’s central and branch campuses remained unaffected, suggesting that the breach had been targeted specifically at the Health Sciences infrastructure, which is often segmented from the broader university network due to the stringent regulatory requirements governing patient health information.
BYOD Ransomware Claims Responsibility for Massive Breach
While the University of New Mexico Health Sciences Center worked to regain its footing, the digital investigation into the origin and nature of the attack began to yield troubling details. Although official channels were initially reticent regarding the specifics of the threat, the emerging ransomware collective known as "BYOD" publicly claimed responsibility for the incident.
The group’s involvement was brought to light by the cybersecurity intelligence firm VenariX, which monitored the actors’ activities on the dark web. According to reports from VenariX, the BYOD group listed the University of New Mexico on its dedicated data leak site. The claims made by the attackers were sweeping and alarming: they alleged that they had successfully compromised 36,000 machines within the university’s network and had exfiltrated a massive volume of sensitive data.
The categories of data reportedly stolen include personally identifiable information (PII) of both students and employees, extensive research data, comprehensive student records, and internal institutional emails. The implications of such a breach are profound. If these claims are verified, the university faces not only the immediate operational cost of recovery but also the long-term legal, regulatory, and reputational challenges associated with a large-scale data breach involving Protected Health Information (PHI) and academic records.
In a taunting message posted to their leak site, the BYOD group stated, "This is your entire network and infrastructure compromised, the entire university COMPLETELY." Such rhetoric is common among modern ransomware operators, who often use the threat of public disclosure—sometimes referred to as "double extortion"—to pressure organizations into paying a ransom. By exfiltrating data, these groups ensure that even if the victim manages to restore their systems from backups, the threat of leaking sensitive information remains a potent weapon.
The scale of the institution affected by this attack cannot be overstated. UNM HSC serves as a cornerstone of healthcare in the region, receiving more than one million patient visits annually. This volume is composed of approximately 900,000 outpatient appointments and roughly 100,000 visits to the emergency room. Furthermore, the academic component of the center is substantial, with an enrollment of 2,670 students as of 2025. The convergence of these two entities—a high-traffic clinical center and a research-intensive academic institution—makes the Health Sciences Center a high-value target for sophisticated cyber-criminal enterprises.
The incident at UNM HSC reflects a broader, global trend in the healthcare sector. Increasingly, cyberattacks are no longer just about the temporary disruption of services; they are about the strategic exploitation of the massive, interconnected databases that modern health systems rely upon. As seen in the recent surge of attacks within the healthcare industry, institutions are finding themselves on the front lines of a digital conflict where the stakes are measured not just in dollars, but in patient safety and the confidentiality of private records.
As the University of New Mexico Health Sciences Center continues its remediation process, the focus will undoubtedly shift toward investigating how the initial access was obtained and strengthening the security posture of its network. The event serves as a stark warning to other academic and medical institutions: in an era of hyper-connectivity, the security of the digital perimeter is inextricably linked to the physical safety of patients and the continuity of essential public services. For the students, staff, and patients of UNM, the coming weeks will likely involve a long road of recovery, password resets, identity monitoring, and the arduous task of piecing together the extent of the data compromise. The incident stands as a significant case study in the vulnerability of critical infrastructure to the persistent and evolving threat of modern ransomware operations.
| Source | : | Finance Poetry |
| Author | : | rifanmuazin |
| Editor | : | Finance Poetry Editorial Team |